Third-Party Poker Software Scandal Raises New Security Concerns

pessi-lamm
01 Oct 2026
Pessi Lamm 01 Oct 2026
Share this article
Or copy link
  • Attackers installed remote-access tools via Jurojin and IntuitiveTables updates.
  • Between 10 and 30 high-stakes players’ PCs compromised, possibly more.
  • Incident highlights crucial need for vigilance in third-party poker software security.
Jurojin and IntuitiveTables were caught up in a targeted security incident involving compromised third-party poker software and remote access to players’ PCs.
A new online poker security scandal has raised concerns about the risks of using third-party poker software after a remote-access tool was allegedly installed on the computers of high-stakes players.

Cybersecurity researcher WolfSec0x0 reported that between 10 and 30 Windows PCs may have been affected. 

The agent reportedly gave an attacker live access to players' screens, potentially exposing hole cards during real-money games. The earliest confirmed activity dates back to March 2024, with some infections remaining active for more than a year.

Jurojin and IntuitiveTables Were Targeted

The two poker software products at the centre of the investigation are Jurojin and IntuitiveTables.
Both are table-management tools designed to help players handle multiple tables, with features including table positioning, hotkeys, HUDs and other poker-specific functions. Jurojin also offers betting tools and real-time overlays.

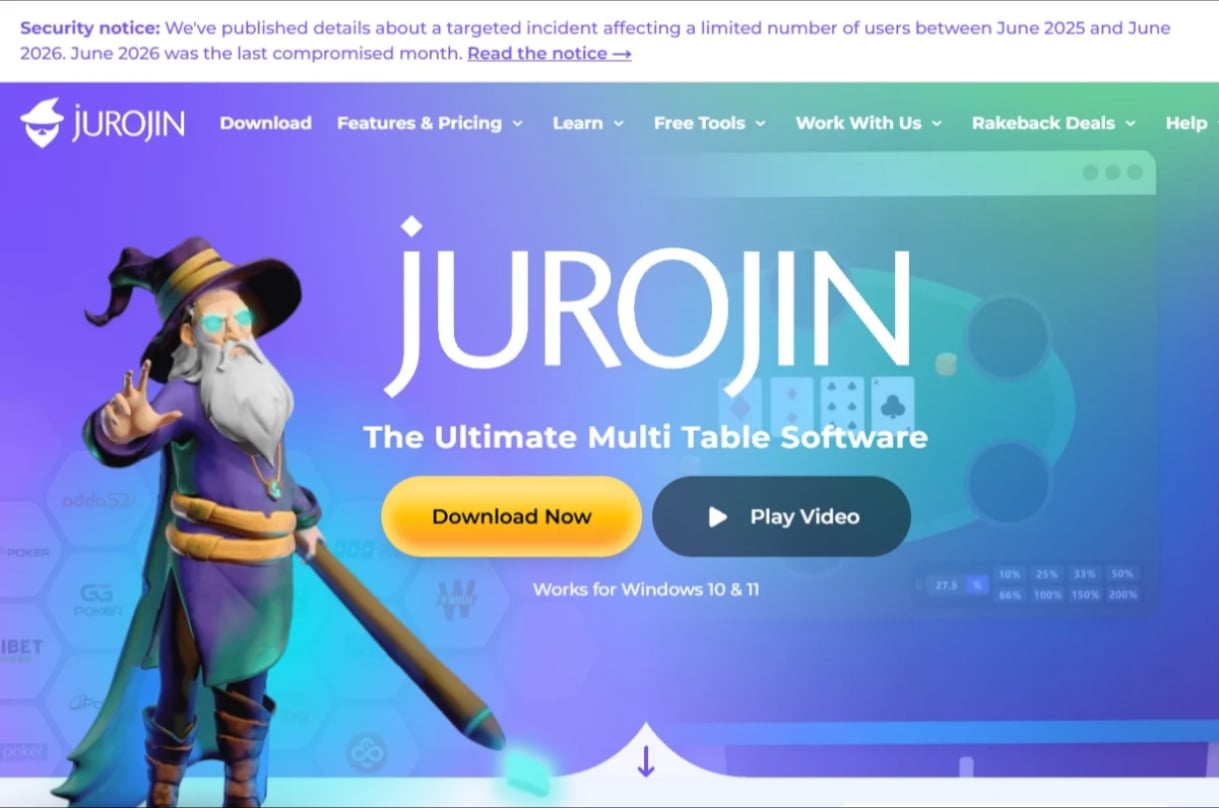
Jurojin has confirmed that its update process was compromised. The company says an attacker intermittently replaced update packages delivered to a specific group of users between June 2025 and June 2026, with some of those packages containing a remote-access tool. Jurojin says the attack was highly targeted and aimed at specific opponents, mostly at high stakes.

IntuitiveTables has also confirmed that it was one of the applications targeted.

undefined
Jurojin has published a security notice detailing the incident and the steps taken to address it.

Mesh Agent Provided Remote Access

The remote-access component was identified as Mesh Agent, part of MeshCentral, a legitimate open-source remote-management platform.

MeshCentral itself is not malware. The problem was the alleged unauthorized installation and use of the software.

According to the researcher, the agent could provide live screen access, mouse and keyboard control, and access to other information on the affected computer. That creates an obvious problem when the screen happens to contain a poker table and a player's hole cards.

Importantly, the poker sites themselves have not been identified as the entry point. The attack appears to have gone through third-party software installed on players' computers.

The Problem May Extend Beyond 30 Players

The players whose computers were compromised are the obvious victims, but they may not be the only ones affected.

If an attacker could view a compromised player's hole cards while they were playing, opponents sitting at the same tables could potentially have been exposed to an unfair information advantage.

There is currently no complete public list of affected games or evidence establishing how many opponents may have been impacted. It is therefore too early to put a number on the wider damage.

The incident does, however, highlight a broader security issue for online poker.

Third-party software has become a normal part of the modern online poker setup. When trusted tools are compromised, the potential consequences can extend beyond the player who installed them.

For Canadian players using third-party poker software, the incident is another reminder that securing the poker client itself may not be enough. The software running alongside it also has to be trusted, and one weak link can ruin it for everybody else.

More Poker News

Upcoming Events